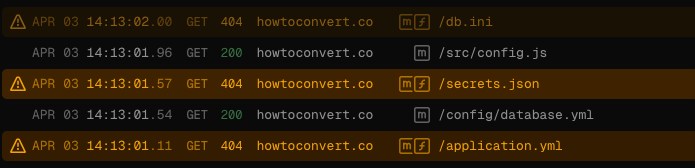
The things vulnerability scanning bots check are crazy. Who on earth stores secret files on the frontend at an endpoint called secrets.json?
Think it's being checked because people actually do it, or just because it would be a goldmine for a hacker if found?
The things vulnerability scanning bots check are crazy. Who on earth stores secret files on the frontend at an endpoint called secrets.json?
Think it's being checked because people actually do it, or just because it would be a goldmine for a hacker if found?